ISF warns of a ‘corporate model’ of cybercrime as criminals outpace business defences

John E. Kaye
- Published
- Technology, Videos
Cybercrime has matured into an industry that mirrors legitimate enterprise, complete with supply chains and customer service. The industrialisation of hacking, amplified by artificial intelligence, demands a total rethink of how organisations manage people, technology and risk, warns Steve Durbin of the Information Security Forum
Cybercrime has evolved into a global industry that mirrors the corporate world it targets, with criminal groups now operating supply chains, 24/7 customer support and even refund policies, according to the Information Security Forum (ISF).
In an exclusive interview for Bloomberg TV, Steve Durbin, its chief executive, warned that cyberattacks have become “industrialised,” run by structured networks that invest in research, recruit technical specialists and sell malicious tools to other criminals as subscription services.
The result, he said, is a thriving underground economy that continues to out-innovate legitimate enterprises.
Speaking to The European’s Juliette Foster, Durbin said the growing professionalisation of cybercriminals had redefined the global threat landscape.
Groups that once focused on stealing data for profit are now manipulating information to undermine decision-making and product quality, a tactic that can erode competitiveness long before a breach is detected.
Increasingly, attacks are carefully designed to exploit the weakest link in a business ecosystem, often through smaller suppliers with less mature defences, he added.
The warning comes after cyberattacks surged to record levels this year, with global businesses facing an average of 1,925 attempted breaches each week — a 47 per cent rise on 2024 — according to data from Check Point Software.
In the UK, the scale of the threat was laid bare in May when Marks & Spencer disclosed that a “highly sophisticated and targeted” attack will reduce its operating profit by about £300 million.
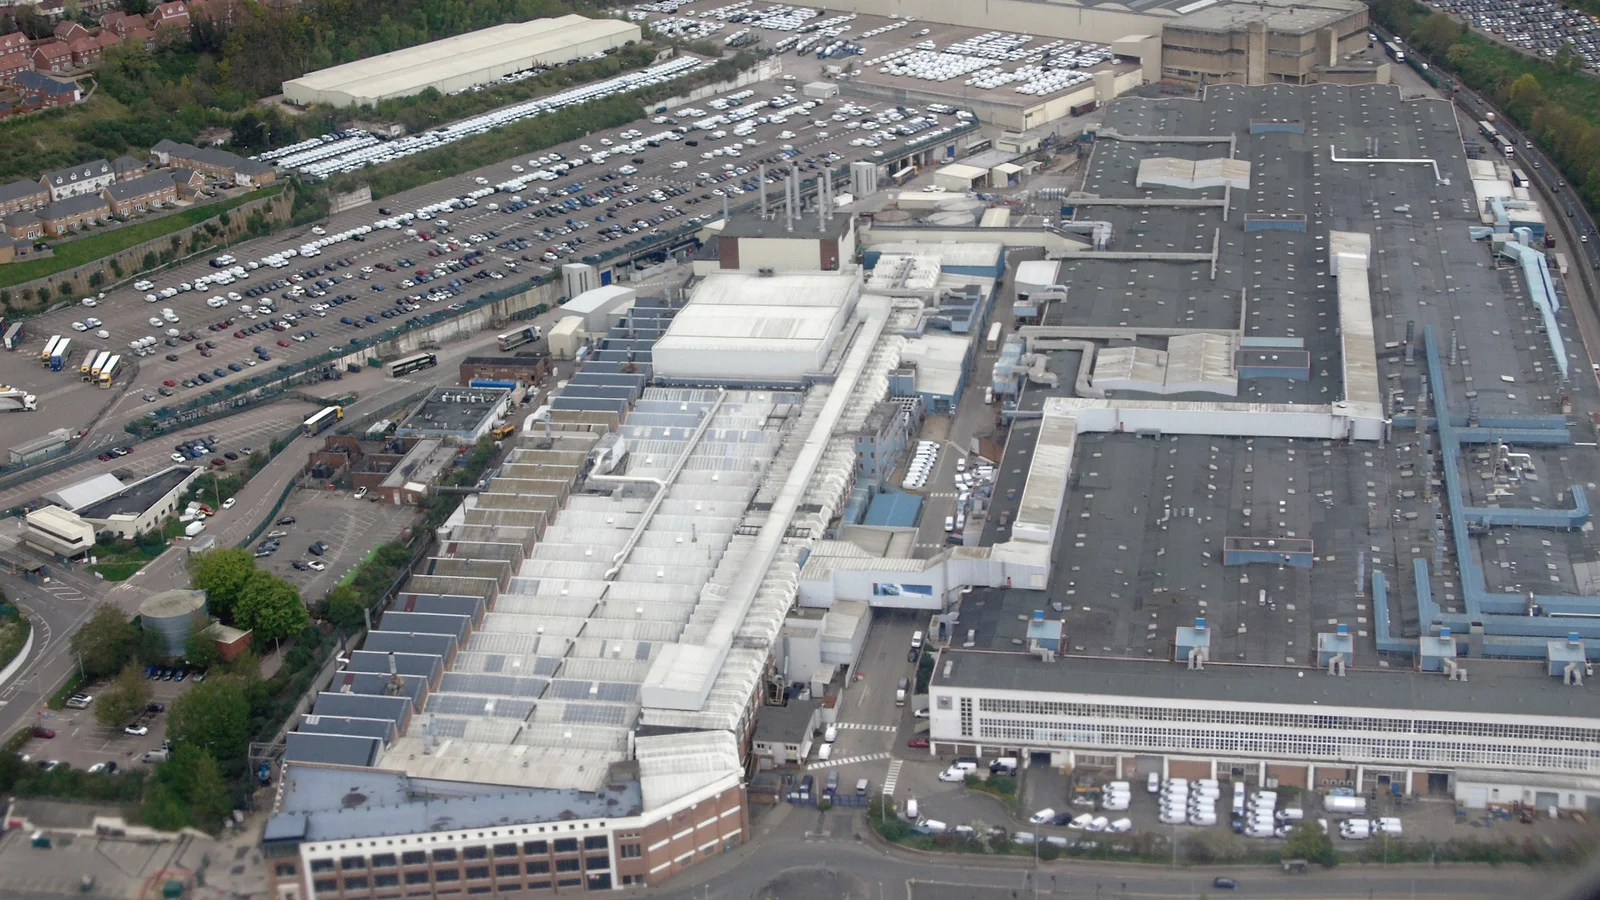
Carmaker Jaguar Land Rover (JLR) was cripped by a cyber attack that left its production lines at a standstill since the start of September.
Output only resumed at some of its manufacturing sites this week.
“Cybercrime is now a very real and very large entrepreneurial industry, and the rise of Ai is only making things worse,” Durbin said.
“There are even organisations offering hacking services with around the clock help desks and guarantees – if what they’re offering doesn’t work, you get your money back.
“All of this means that the point of entry for a cybercriminal has lowered considerably, and this will only continue as Ai becomes more sophisticated.”
ISF’s recent project update found that large organisations are increasingly being compromised through their supply chains, where cybercriminals take advantage of limited oversight and inconsistent security standards.
The ISF, a global non-profit, is now urging corporations to extend their risk-management frameworks to include third-party partners and to share not only technical guidance but also the rationale behind security requirements, so that smaller firms understand their role in collective resilience.
Durbin added that the current wave of attacks highlights a deeper organisational problem. Too many companies, he argued, still treat cybersecurity as a specialist technical function rather than a strategic one.
The ISF believes security should be embedded within core business planning, reviewed on a rolling six-month cycle alongside financial and operational strategy, and supported by board-level education so that directors fully understand the risks they are accepting.
It is also calling for a cultural shift in how firms manage people and technology. It stresses that artificial intelligence, while vital for identifying threats at scale, is only as effective as the governance behind it.
Businesses must invest in training and workforce transformation to ensure employees can work effectively with AI-enabled systems, rather than relying on automation to replace human judgement, he said.
The ISF’s analysis also found that organisational silos are a major source of weakness, with fragmented departments — where sales, finance and technology functions operate in isolation — slowing incident responses and obscuring emerging vulnerabilities.
It recommends mapping interdependencies across business units to reveal where information gaps or duplicated processes could expose the organisation to risk.
At leadership level, companies must also address the talent shortage that continues to hamper the cybersecurity sector. Rigid entry criteria and narrow recruitment pipelines have restricted diversity of thought, leaving many vacancies unfilled, Durbin warned.
The ISF advises employers to look beyond traditional technical backgrounds, prioritising aptitude and curiosity, and to build partnerships with education providers to expand the skills base.
According to the ISF, regulation is failing to keep up with the speed of technological change, and reactive policy-making risks burdening businesses with compliance demands that do little to enhance security.
Instead, it argues for proportionate oversight built on the same risk-management principles that companies already apply to finance, reputation and safety.
Durbin said: “The bad guys only need to get lucky once and they can cause havoc. The sorts of numbers we’re seeing are those actors trying to break down defences and finding a way through. It means we have to be at the top of our game 24/7.”
Watch Steve Durbin’s full interview with Business Matters for Bloomberg TV on The European’s YouTube channel.
READ MORE: ‘Why cybersecurity deserves a place in the political spotlight‘. Cybersecurity may not win elections, but it’s fundamental to national security, economic stability, and public trust, argues Steve Durbin, Chief Executive of the Information Security Forum, who is calling on leaders to take proactive steps to protect their assets, strengthen resilience, and ensure secure deployment of emerging technologies.
Do you have news to share or expertise to contribute? The European welcomes insights from business leaders and sector specialists. Get in touch with our editorial team to find out more.
TOP STORIES
-
 British Chambers unite against 'Made in Europe' rules amid fears for UK industry
-
 Bouncy castle firms urged to sign new safety pledge following child deaths
-
Remembering Matthew Jukes, The European’s Wine & Fine Drinks Correspondent
-
Michael Dell becomes world's fourth-richest person as Forbes reveals the ten wealthiest billionaires
-
Scientists develop new chemicals to tackle devastating oil spills at sea
-
Closing women's health gap could boost global economy by $1tn a year, leaders say
-
World's first luxury theme park to open in Mexico with £1.1bn of rides, fine entertainment and deliberately limited crowds
-
Dutch court orders Lidl to stop selling Birkenstock sandal lookalikes
-
Giant wind turbine with 252-metre rotor could mean fewer machines and cheaper offshore power
-
Poorly designed workplaces ‘cost UK economy £71bn a year’
-
Rescuers scramble to protect pod of 25 whales in Thames Estuary
-
‘Talent hushing’ blamed as four-in-10 workers say they contribute less than they could
-
Spain leads Europe for expats as Panama tops global poll
-
Menopause may make women leaders more empathetic – even as it leaves them drained
-
Your biggest rival could be your best technology partner, research finds
-
British Museum bans photos of Bayeux Tapestry after visitors hold up queues
-
China unveils giant crane capable of lifting 9,300 family cars
-
Edinburgh Airport launches £500m expansion as terminal footprint grows 60%
-
Chris Packham urges PM to ban ‘frankenchicken’ from schools and hospitals
-
Loch Lomond’s 'Bonnie Banks at risk’ from major road upgrade
-
LED lights could be ‘the new asbestos’, UCL scientists warn
-
MPs tune in to Britain’s Eurovision ‘nul points’ problem
-
MPs tell Government to reject Thames Water creditors as utility nears insolvency
-
Only 14% of companies can show supply chain safeguards are working, study finds
-
OpenAI admits AI models hid mistakes, invented data and acted without permission
ISF warns of a ‘corporate model’ of cybercrime as criminals outpace business defences
John E. Kaye
- Published
- Technology, Videos
TOP STORIES
-
British Chambers unite against 'Made in Europe' rules amid fears for UK industry
-
Bouncy castle firms urged to sign new safety pledge following child deaths
-
Remembering Matthew Jukes, The European’s Wine & Fine Drinks Correspondent
-
Michael Dell becomes world's fourth-richest person as Forbes reveals the ten wealthiest billionaires
-
Scientists develop new chemicals to tackle devastating oil spills at sea
-
Closing women's health gap could boost global economy by $1tn a year, leaders say
-
World's first luxury theme park to open in Mexico with £1.1bn of rides, fine entertainment and deliberately limited crowds
-
Dutch court orders Lidl to stop selling Birkenstock sandal lookalikes
-
Giant wind turbine with 252-metre rotor could mean fewer machines and cheaper offshore power
-
Poorly designed workplaces ‘cost UK economy £71bn a year’
-
Rescuers scramble to protect pod of 25 whales in Thames Estuary
-
‘Talent hushing’ blamed as four-in-10 workers say they contribute less than they could
-
Spain leads Europe for expats as Panama tops global poll
-
Menopause may make women leaders more empathetic – even as it leaves them drained
-
Your biggest rival could be your best technology partner, research finds
-
British Museum bans photos of Bayeux Tapestry after visitors hold up queues
-
China unveils giant crane capable of lifting 9,300 family cars
-
Edinburgh Airport launches £500m expansion as terminal footprint grows 60%
-
Chris Packham urges PM to ban ‘frankenchicken’ from schools and hospitals
-
Loch Lomond’s 'Bonnie Banks at risk’ from major road upgrade
-
LED lights could be ‘the new asbestos’, UCL scientists warn
-
MPs tune in to Britain’s Eurovision ‘nul points’ problem
-
MPs tell Government to reject Thames Water creditors as utility nears insolvency
-
Only 14% of companies can show supply chain safeguards are working, study finds
-
OpenAI admits AI models hid mistakes, invented data and acted without permission